
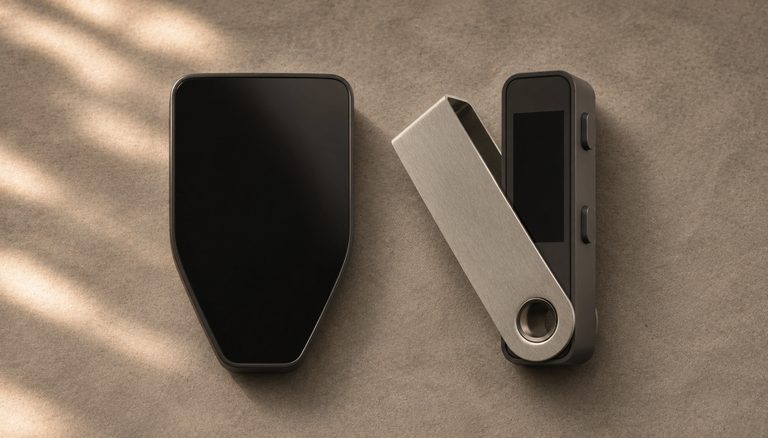
Choosing between Trezor and Ledger is the most common decision new Bitcoin self-custody users face. Both companies have been around for over a decade, both make solid hardware, and both have passionate communities defending their choice. But the differences between these two ecosystems are real, significant, and worth understanding before you commit your bitcoin to either platform.
This comparison covers every current model from both companies, analyzes the fundamental security architecture differences, and gives you a clear recommendation based on your priorities.
Updated 7 November 2026: prices are from the makers’ own stores (checked 3 November 2026). The lineup now includes the Trezor Safe 7 and the Ledger Nano Gen5, Ledger’s app is called Ledger Wallet (Ledger Live until October 2025), Trezor Safe devices make a 20-word backup by default, Trezor Suite’s CoinJoin feature ended in June 2024, and the buying advice reflects an October 2026 incident at an authorised reseller.
The Current Lineup: Every Model Compared
Both Trezor and Ledger offer tiered product lines ranging from budget-friendly to premium. Here is what each sells in November 2026, at the prices on their own stores.
Trezor’s Current Models
Trezor Safe 3 ($59) is the entry-level Trezor. It is compact (59 × 32 × 7.4 mm, 14 g), with a small monochrome OLED display (0.96 inches, 128×64 pixels), two buttons and USB-C. Despite being the cheapest option, it includes an EAL6+ certified secure element, the same chip as the Safe 5. A Bitcoin-only edition leaves out all code for other coins, so there is less code that could hold a bug.
Trezor Safe 5 ($129) steps up significantly in usability. The 1.54-inch color touchscreen with haptic feedback replaces the buttons, and the face is protected by Gorilla Glass 3. It uses the same EAL6+ secure element, but the better screen makes a real difference if you use your hardware wallet regularly rather than as set-and-forget cold storage. Dimensions are 65.9 × 40 × 8 mm at 23 grams. Read our Trezor Safe 5 review.
Trezor Safe 7 ($249) is Trezor’s newest and largest model. Trezor lists a 2.5-inch color touchscreen, encrypted Bluetooth, Qi2-compatible wireless charging and a second secure chip, TROPIC01, which it presents as an independently auditable secure element. It is the first Trezor you can use from your phone without a cable. We have not reviewed it hands-on.
All three make a 20-word backup by default, in a standard called SLIP-39. It restores on every Trezor except the original Trezor One, and on wallets such as Sparrow, Electrum and Keystone, but not on Ledger or Coldcard. If you might switch brands, choose a 12- or 24-word BIP39 backup from Trezor Suite’s backup format option when you create the wallet.

Ledger’s Current Models
Every Ledger makes a 24-word BIP39 backup, runs Ledger’s closed-source operating system on a secure element, and is managed with the Ledger Wallet app (called Ledger Live until October 2025).
Ledger Nano S Plus ($69) is Ledger’s entry point: a small OLED display (128×64), two buttons, USB-C and no Bluetooth. Its ST33K1M5 secure element is certified EAL6+, the same chip as Ledger’s touchscreen models.
Ledger Nano X ($99) adds Bluetooth and a built-in battery, so it works with the Ledger Wallet phone app. It has the same 128×64 OLED display as the Nano S Plus, but an older secure element, the ST33J2M0, certified EAL5+, one level below Ledger’s newer chip. Read our Ledger Nano X review.
Ledger Nano Gen5 ($179), launched in October 2025, is Ledger’s newest Nano: a 2.8-inch E Ink touchscreen, USB-C, Bluetooth and NFC, with the EAL6+ ST33K1M5 chip. Its larger screen makes full addresses easier to read than on earlier Nanos. It ships with a Ledger Recovery Key card, which Ledger says works alongside your paper backup, not instead of it. We have not reviewed it hands-on.
Ledger Flex ($249) has a 2.8-inch E Ink touchscreen, Bluetooth, NFC and the EAL6+ chip. It shares the Stax’s security architecture without the curved display. Read our Ledger Flex review.
Ledger Stax ($399) is Ledger’s top model. It has a 3.7-inch curved E Ink touchscreen with 16 shades of gray, Qi wireless charging, NFC and the EAL6+ chip. The E Ink display can show a custom lock screen image even when powered off. You pay for the screen and the design; the security is the same as the Flex.
In October 2026 Ledger also announced the Ledger Atom, an Android-based device with a secure element running Ledger OS. It can only be reserved so far, with delivery estimated for mid-2027, so it isn’t in this comparison.
Head-to-Head Comparison Table
| Device | Price (Nov 2026) | Screen | Connectivity | Secure element | Open-source firmware | Bitcoin-only edition | Default backup |
|---|---|---|---|---|---|---|---|
| Trezor Safe 3 | $59 | 0.96" mono OLED, 2 buttons | USB-C | Yes, EAL6+ (OPTIGA) | Yes | Yes | 20 words (SLIP-39) |
| Trezor Safe 5 | $129 | 1.54" color touch | USB-C | Yes, EAL6+ (OPTIGA) | Yes | Yes | 20 words (SLIP-39) |
| Trezor Safe 7 | $249 | 2.5" color touch | USB-C, Bluetooth, Qi2 | Yes, OPTIGA + TROPIC01 | Yes | Yes | 20 words (SLIP-39) |
| Ledger Nano S Plus | $69 | Small OLED, 2 buttons | USB-C | Yes, EAL6+ (ST33K1M5) | No | No | 24 words (BIP39) |
| Ledger Nano X | $99 | Small OLED, 2 buttons | USB-C, Bluetooth | Yes, EAL5+ (ST33J2M0) | No | No | 24 words (BIP39) |
| Ledger Nano Gen5 | $179 | 2.8" E Ink touch | USB-C, Bluetooth, NFC | Yes, EAL6+ (ST33K1M5) | No | No | 24 words (BIP39) |
| Ledger Flex | $249 | 2.8" E Ink touch | USB-C, Bluetooth, NFC | Yes, EAL6+ (ST33K1M5) | No | No | 24 words (BIP39) |
| Ledger Stax | $399 | 3.7" curved E Ink touch | USB-C, Bluetooth, NFC, Qi | Yes, EAL6+ (ST33K1M5) | No | No | 24 words (BIP39) |
Prices from the makers’ own stores, checked 3 November 2026 (Nano Gen5 from Ledger’s launch notice). Every model also supports a passphrase, and Trezor’s SLIP-39 standard can split a backup into several shares (multi-share); Ledger has no equivalent. The Trezor Safe 7 and Ledger Nano Gen5 rows are from the makers’ specifications; we have not tested either hands-on.
Security Model Comparison: The Fundamental Difference
This is where the Trezor vs Ledger debate gets genuinely interesting, because these companies have made fundamentally different architectural decisions about how security should work.
Trezor’s Security Philosophy: Trust Through Transparency
Trezor’s firmware is open source: anyone with the technical skill can audit it, compile it from source and check the result against the official firmware release. The argument is straightforward: you should not have to trust the manufacturer; you should be able to verify. As we have explored in our analysis of why open source hardware wallets matter, this transparency is a core tenet of Bitcoin’s “don’t trust, verify” philosophy.
The Safe 3, Safe 5 and Safe 7 include an EAL6+ certified secure element (the OPTIGA Trust M chip from Infineon). This was a significant shift. Earlier Trezor models lacked a secure element entirely, which made them vulnerable to physical extraction if an attacker had the device in hand: in 2022 a hardware hacker pulled the seed out of an old Trezor One running outdated firmware. The secure element protects the seed from physical extraction while the open-source firmware handles all the signing logic. The chip’s own code is not open source; Trezor chose a chip that is “NDA-free”, which lets it publish all of its own code that talks to it. The Safe 7 adds a second chip, TROPIC01, which Trezor presents as an independently auditable secure element.
Trezor’s approach to the secure element is worth understanding: the chip guards a secret that it releases only for the right PIN, and that secret unlocks your keys, kept encrypted on a general-purpose microcontroller where the open-source firmware does the signing. This keeps the “black box” part of the device small, while the signing logic stays auditable.
Ledger’s Security Philosophy: Secure Element First
Ledger takes the opposite approach. Their entire security model is built around proprietary secure element chips, and the firmware running on them is closed source. Ledger argues that disclosing secure element firmware code would actually reduce security by giving attackers a roadmap. For a deeper dive into the implications, see our complete Ledger security analysis.
Instead of open-source transparency, Ledger relies on third-party security audits and its own closed operating system, Ledger OS (formerly called BOLOS), running inside the certified secure element. Every current Ledger except the Nano X uses the ST33K1M5 chip, certified EAL6+, the same level as Trezor’s chip; the Nano X’s ST33J2M0 is certified EAL5+.

The Ledger Recover controversy of 2023 highlighted the tension in this model. Ledger Recover is an optional paid service: if you sign up and approve it on the device, it encrypts your seed, splits it into three fragments held by Ledger, Coincover and EscrowTech, and lets you recover with two of them after an identity check. Critics argued it showed that Ledger’s closed firmware can be updated to export a seed, and that users cannot verify it never happens without their consent. Ledger replied that Recover is opt-in and needs your PIN and approval on the device. In principle any hardware wallet’s firmware could be changed to export a seed; the debate is over how much you can verify, which open-source firmware makes easier.
Which Security Model Is Better?
Neither approach is objectively wrong, but they optimize for different threat models:
- Trezor is better if you are worried about hidden firmware behavior or backdoors. You can verify the code yourself or rely on the community of reviewers who do.
- Ledger is better if you are primarily worried about physical extraction attacks by sophisticated adversaries with specialized equipment. Ledger has used secure elements for longer, though Trezor’s current models now have an EAL6+ secure element too.
Neither model protects you from a device that was tampered with before it reached you; that’s why where you buy matters (see the FAQ below). For most Bitcoiners, the open-source argument carries more weight: you are far more likely to face malicious or manipulated software than a nation-state level physical chip extraction attack. And as our hardware wallet comparison chart shows, there are compelling open-source alternatives from other manufacturers too.
Open Source Analysis: What Can You Actually Verify?
The “open source” label requires nuance. Here is exactly what you can and cannot verify with each platform.
Trezor: What Is Open
- Firmware: Open source on GitHub (trezor-firmware repository). You can read all the code that runs on the general-purpose microcontroller.
- Hardware design: Trezor publishes hardware design files on GitHub (trezor-hardware).
- Trezor Suite (desktop app): Source published on GitHub under Trezor’s own reference licence, which lets you read it but not redistribute it: the companion app is auditable, but not open source in the strict sense.
- Reproducible builds: You can compile firmware from source and verify it matches the official release file, signature aside. Trezor Suite’s firmware hash check then confirms an up-to-date device is running that release.
- Secure element firmware: The OPTIGA Trust M chip runs proprietary Infineon code. This is the closed component in the Trezor stack, and it is limited to protecting the seed. The Safe 7’s second chip, TROPIC01, is presented by Trezor as independently auditable.
Ledger: What Is Open
- Firmware: Closed source. Ledger OS, the operating system running the core security logic, cannot be audited by the public.
- Individual app code: The Bitcoin app and most coin-specific apps are open source. But they run on top of the closed Ledger OS.
- Ledger Wallet app (formerly Ledger Live), desktop and mobile: Partially open source.
- Hardware schematics: Not published.
- Secure element firmware: Closed source, and this is where the actual security-critical code runs.
The practical implication: with Trezor, a sufficiently motivated individual can audit nearly the entire stack. With Ledger, you are trusting their internal security team and their third-party auditors. Both approaches have worked so far. Neither company has had a firmware-level exploit that resulted in user fund losses. But philosophically, they represent very different trust models, and for a device designed to protect potentially life-changing amounts of bitcoin, the trust model matters.
Privacy Implications
Privacy is an often-overlooked factor in the hardware wallet choice, but it matters significantly for Bitcoiners who take privacy seriously.
Trezor’s Privacy Profile
- Companion software: By default Trezor Suite looks up your addresses on servers run by Trezor, which Trezor says don’t log your activity; you can point it at your own Bitcoin node through an Electrum server instead. The desktop app also has built-in Tor support.
- Data collection: Trezor Suite’s source code is public, so what it sends is auditable.
- Data incidents: In January 2024 someone accessed the third-party support portal Trezor used, possibly exposing names and emails of up to 66,000 support contacts (no funds affected, per Trezor’s notice of 19 January 2024). In August 2026 Trezor’s shipping provider, ShipMonk, reported a breach that exposed the names, contact details and, for most of them, shipping addresses of 80,689 customers (Trezor’s notice, updated 4 September 2026). In September 2026 attackers broke into Trezor’s newsletter provider, exported 347,149 subscriber email addresses and sent a fake “security alert” asking for wallet backups (our advisory).
- Third-party wallet support: Excellent compatibility with Sparrow, Electrum and other wallets that bypass Trezor’s servers entirely.
- CoinJoin: Trezor Suite’s CoinJoin feature ended on 1 June 2024, when the coordinator it relied on shut down. Tor and coin control remain.
Ledger’s Privacy Profile
- Companion software: The Ledger Wallet app (formerly Ledger Live) looks up each of your addresses on Ledger’s own servers to show your balance, so Ledger’s infrastructure sees your entire transaction history and balance, even though Ledger says your extended public key (xpub) stays on your computer.
- Data breach history: The 2020 Ledger customer database breach exposed names, physical addresses, phone numbers and email addresses of about 272,000 customers. This led to targeted phishing campaigns and reported physical threats against known Ledger owners. In January 2026 Ledger’s payments partner Global-e reported that customer names and contact details from Ledger.com orders had been copied; Ledger said no payment data or recovery phrases were involved.
- Third-party wallet support: Good compatibility with Sparrow, Electrum and other wallets that bypass Ledger’s servers. With a third-party wallet connected to your own node, those lookups never reach Ledger.
These breaches show that buying a hardware wallet creates a data trail, and that customer data is a high-value target for criminals. Buy from the maker’s own store and, to limit what a future leak could reveal, have the device shipped to a PO box or pickup point rather than your home, whichever brand you choose.

Software Ecosystem: Trezor Suite vs Ledger Wallet
Both companies provide companion desktop and mobile applications that serve as the primary interface for their hardware wallets.
Trezor Suite
- Desktop application (Windows, macOS, Linux) and web interface
- Built-in coin control for UTXO management
- Tor integration for network-level privacy
- Public, auditable source code
- Clean, focused interface that prioritizes Bitcoin functionality
- Connect to your own full node for maximum sovereignty
Ledger Wallet (formerly Ledger Live)
- Desktop (Windows, macOS, Linux) and mobile (iOS, Android) applications; the phone app pairs over Bluetooth with the Nano X, Nano Gen5, Flex and Stax
- Polished interface with buying, swapping and many extras for other coins built in
- Genuine Check confirms during setup that the device is authentic
- Needed for firmware updates and for installing apps on the device
Trezor Suite is more Bitcoin-focused and privacy-oriented. Ledger Wallet has more features, but it exposes your addresses and balances to Ledger’s servers unless you use a third-party wallet with your own node. For bitcoin, Trezor Suite is the clear winner; most of Ledger Wallet’s extras serve other coins.
Both devices work excellently with third-party wallets like Sparrow Wallet, which is the recommended option for privacy-conscious Bitcoiners regardless of which hardware wallet they choose.

Unique Features: What Sets Each Apart
What Trezor Offers That Ledger Doesn’t
- Multi-share backup (SLIP-39): Split your backup into several shares where any M of N can rebuild the wallet, for example any 2 of 3 kept in three separate places. Ledger has no equivalent. It’s easy to get wrong in a way that locks you out, so start with a single backup. We cover this in our guide to seed phrase security.
- Bitcoin-only firmware: An edition that contains no code for other coins. If you only hold bitcoin, less code on the device means fewer places for bugs.
- Reproducible builds: Rebuild an official firmware release from the published source code and check you get the same file, signature aside. Ledger’s closed operating system offers nothing comparable.
What Ledger Offers That Trezor Doesn’t
- Bluetooth across the range: The Nano X ($99), Nano Gen5, Flex and Stax all sign from your phone without a cable. Trezor offers Bluetooth only on the Safe 7 ($249).
- A backup most wallets read: 24 BIP39 words by default, which restore on most other brands.
- Ledger Recover: Optional paid seed backup service through third-party custodians. Controversial, but available for users who want a safety net against losing their paper backup.
- E Ink displays (Nano Gen5, Flex and Stax): The screen keeps showing an image when the device is off, and you can set your own lock screen.
- NFC (Nano Gen5, Flex and Stax): Used with Ledger’s Recovery Key card.

Build Quality and Daily Use Experience
At the budget tier, the Trezor Safe 3 ($59) and Ledger Nano S Plus ($69) are both compact, plastic-bodied devices with small monochrome screens and two buttons. Neither feels premium, but both are functional and reliable. On either one, checking a long address means scrolling through it.
In the middle, the choice widens. The Trezor Safe 5 ($129) has a color touchscreen behind Gorilla Glass: verifying addresses and confirming transactions is pleasant rather than tedious. The Ledger Nano X ($99) keeps the older screen-and-buttons design but adds Bluetooth for phone use. The Ledger Nano Gen5 ($179) combines a 2.8-inch E Ink touchscreen with Bluetooth. If signing from your phone matters most, look at the Ledgers; if on-device address checking with open firmware matters most, the Safe 5 wins.
At $249 the Trezor Safe 7 and the Ledger Flex meet head-on: both have large touchscreens and Bluetooth, with open firmware on the Trezor and E Ink on the Ledger. The Ledger Stax ($399) has the largest screen of all, with the same chip and security as the Flex: there you pay for the screen and the design. The Safe 7 is different: it adds a second secure chip, TROPIC01, which the Safe 3 and Safe 5 don’t have.
Multisig Compatibility
If you are setting up a 2-of-3 multisig or any multi-signature configuration, both Trezor and Ledger work well as signing devices. They are both compatible with major multisig coordinators like Sparrow, Electrum and Nunchuk. Multisig is for once you’re comfortable with a single device; set it up later, not first.
Many advanced Bitcoiners recommend using devices from different manufacturers in a multisig setup. A 2-of-3 multisig with one Trezor, one Ledger, and one Coldcard provides vendor diversity. A firmware bug in one manufacturer’s device does not compromise your funds because the other signing devices use completely different firmware stacks. This is one of the strongest arguments for multisig in general, and it means the Trezor vs Ledger decision does not have to be either/or. You can use both.
For more on multisig setups and the rationale behind vendor diversity, see our comprehensive guide on Bitcoin multisig from beginner to expert.
Which Should You Buy?
After comparing every angle, here are clear recommendations based on user profiles.

Buy Trezor If:
- You are a Bitcoin-only holder. Bitcoin-only firmware, Shamir backup, and open-source code make Trezor the natural choice for Bitcoiners who do not hold altcoins.
- Open source matters to you. If “don’t trust, verify” is more than a slogan, Trezor is the only one of these two whose wallet firmware you can read and verify yourself.
- You want a multi-share backup. Among these two brands only Trezor offers SLIP-39 shares for spreading a backup across several locations.
- Privacy is a priority. Trezor Suite’s Tor integration, coin control and public source code give it a meaningful edge for privacy-conscious users.
- You’re happy with a 20-word backup, or you choose 12 or 24 BIP39 words at setup so the backup restores on other brands too.
- Best value pick: Trezor Safe 3 ($59) with Bitcoin-only firmware. Hard to beat for focused, no-nonsense Bitcoin security.
Buy Ledger If:
- You want to sign from your phone. The Nano X, Nano Gen5, Flex and Stax all connect to the Ledger Wallet phone app over Bluetooth, from $99. On Trezor’s side, only the Safe 7 ($249) has Bluetooth.
- You want a backup that restores almost anywhere. Ledger’s 24 BIP39 words restore on most other brands.
- You want the widest app features, and you’re comfortable trusting closed-source firmware from a long-established company.
- You want a large screen. The Nano Gen5, Flex and Stax have large E Ink touchscreens that make a full address easy to check.
- Best value pick: Ledger Nano X ($99) for signing from your phone over Bluetooth. The Nano Gen5 ($179) adds a 2.8-inch E Ink touchscreen and a newer, EAL6+ chip.
The Overall Recommendation
For most Bitcoiners reading this site: Trezor Safe 5 ($129) with Bitcoin-only firmware is the best overall pick, and it is the device our free course recommends to beginners. You get open-source firmware, an EAL6+ secure chip, a modern touchscreen and excellent compatibility with privacy-focused tools. Know that it makes a 20-word SLIP-39 backup by default: if you may switch brands one day, choose a 12- or 24-word BIP39 backup when you create the wallet.
If budget is the primary concern, the Trezor Safe 3 ($59) has the same secure chip and firmware for less than half the price. You are mostly paying for the better screen and touchscreen interface.
Whichever you choose, write your recovery words down (20 by default on a Trezor, 24 on a Ledger), consider stamping them in metal rather than relying on the paper card, and test the backup. Our guide to the recovery phrase explains how. Once you’re comfortable, a passphrase (25th word) adds a layer, but it’s easy to get wrong in a way that locks you out, so learn it before you rely on it. Check our self-custody checklist for a complete setup guide that applies regardless of which hardware wallet you own.
Frequently Asked Questions
Has Trezor or Ledger ever been hacked?
No remote attack on either company’s devices has stolen keys. Physical attacks on older Trezors are real: in 2022 a hardware hacker extracted the seed from an old Trezor One running outdated firmware, with the device in hand. Both companies have leaked customer data: Ledger’s 2020 database breach exposed the details of about 272,000 customers (not their funds), leading to targeted phishing and physical threats, and Ledger’s payments partner Global-e leaked names and contact details in January 2026; in January 2024 someone accessed the support portal Trezor used, possibly exposing names and emails of up to 66,000 support contacts. In 2026 two of Trezor’s suppliers were breached too: its shipping company in August (names, contact details and, for most, shipping addresses of 80,689 customers) and its newsletter provider in September (347,149 email addresses). In October 2026 a hidden implant that copies the recovery words was found in a Ledger sold by an authorised reseller; see “Should I buy directly from the manufacturer?” below.
Can I use Trezor and Ledger together in a multisig?
Yes, and it is actually recommended by many security experts. Using hardware wallets from different manufacturers in a multisig setup provides vendor diversity. If a critical firmware vulnerability is found in one manufacturer’s devices, your funds remain protected by the other signing devices. A 2-of-3 multisig with a Trezor, a Ledger, and a third device from another manufacturer is one of the strongest self-custody configurations available.
Is Bluetooth on Ledger a security risk?
The Bluetooth connection carries only public data: unsigned transactions in, signed transactions out, and your addresses. The private keys never leave the secure element, and Ledger encrypts the link. It does add a wireless interface that USB-only devices don’t have, which is why some people avoid it on principle; the same applies to the Trezor Safe 7. If you prefer no wireless link at all, choose a USB-C-only model from either maker, or use the USB-C connection on a Bluetooth-capable Ledger.
Which wallet has better customer support?
Both run official help centres and support tickets from their own websites, trezor.io and ledger.com. Reach support only from there: fake support accounts on social media and in search ads are one of the most common ways owners lose funds. Real support never asks for your recovery words, whoever claims to be asking.
Should I buy directly from the manufacturer?
Yes. Buy new, from the maker’s own store: trezor.io or ledger.com. In October 2026 Ledger confirmed a hidden implant that copied the recovery words during setup in a device sold by CryptoBilis, an authorised reseller of Ledger and Trezor in Southeast Asia, and Trezor said it had a credible report, not yet examined in its lab, of a similar implant in a Safe 5 from the same reseller (our advisory). The maker’s authenticity check can’t catch every physical change, so buying from the maker removes the middle link. If the maker doesn’t deliver to your country, use a reseller listed on the maker’s own website and check our security advisories for that reseller first. Avoid Amazon, eBay and other marketplaces, even listings labelled “official store”, and never buy second-hand.
What happens if Trezor or Ledger goes out of business?
Your bitcoin is secured by your recovery words, not by the company. If either manufacturer disappeared tomorrow, a Ledger’s 24 BIP39 words would restore in most wallets and hardware wallets. A Trezor’s default 20-word backup uses SLIP-39, which restores on wallets that support it, such as Sparrow, Electrum and Keystone; the SLIP-39 standard is public and its recovery tools are open source, independent of Trezor. This is another advantage of open standards: the recovery tools are not locked to a single company’s ecosystem.


